Democrat tycoon buys top home security company — to train his business partner's AI


Customers who trust ADT to protect their homes will soon have their security systems invaded by AI. The company was recently bought by another group with close ties to OpenAI, and an artificial intelligence overhaul is all but inevitable.

Popular home security service ADT was acquired last month by Thrive Holdings, a company backed by OpenAI. Thrive Holdings is a spinoff of Thrive Capital, the venture capital firm founded by Democrat tycoon Joshua Kushner, the younger brother of President Trump’s former senior adviser Jared Kushner.

The move could ultimately give Thrive Holdings and OpenAI access to user data to train and optimize OpenAI’s GPT models.

Despite hints that AI investments are drying up, leading to a possible collapse, Joshua is one of the more bullish venture capitalists when it comes to AI. Instead of short-term gains, he has his eyes set on the big picture, writing in a letter obtained by Bloomberg:

“It is difficult to overstate the magnitude of the opportunity. It would also be a grave error in our minds to let excitement weaken our investment discipline.” He added, “Within Silicon Valley in particular, the industry can become fixated on hyper-incremental technological turns rather than where the technology ultimately leads.”

This stance comes as no surprise, as Kushner’s company Thrive Holdings is tightly intertwined with one of the largest, most powerful frontier AI platforms in the world. Nearly a year ago, OpenAI took an ownership stake in Thrive Holdings, tying them together as partners.

In the official press release, the AI giant openly admitted that, “OpenAI will embed research, product, and engineering teams inside Thrive Holdings’ companies to boost speed, accuracy, and cost efficiency while strengthening service quality. The work will establish a repeatable model that can expand across other industries.”

In the same release, Kushner added, “The businesses we acquire represent the right reward systems for this evolution, bringing together industry expertise and real-world data that can help improve models on specific tasks and capabilities.”

In other words, future acquisitions following the December 2025 partnership — like ADT — would be made specifically to further AI development and expand AI features across their brands. They want to use their companies to make OpenAI’s models smarter and more effective.

Thrive Holdings will pay $15.3 billion in cash to gobble up one of the most trusted names in home security — a badge of honor it earned over 150 years after it was founded in 1874. To finalize the deal, Thrive Holdings will buy all public shares of ADT at $10 per unit, officially taking it off the New York Stock Exchange to turn it into a private company.

RELATED: OpenAI called its chatbot an 'existential risk.' Now it faces a legal ultimatum from this red state
Khanchit Khirisutchalual/Getty Images

The move could ultimately give Thrive Holdings and OpenAI access to user data to train and optimize OpenAI’s GPT models. In exchange, users would likely get additional AI-powered features to shore up their home security beyond what ADT currently offers.

Now before you unplug your system and throw it out with this week’s garbage, note that nothing about the service will change overnight. In fact, the company made a strong promise that, “ADT’s data and privacy policies will remain unchanged, and no new data sharing will occur without customer permission.”

That’s a good start.

One of Thrive Holdings’ co-founders reiterated the same sentiment, stating, “Protecting customers’ homes also means protecting their data. Thrive Holdings is committed to upholding the highest standards of privacy and cybersecurity to protect the information that customers entrust to ADT.”

If you’re an ADT customer, there’s nothing you need to do today. Your service will remain active with the same policies in place. However, it would be a good idea to keep an eye out for future communications as the new ADT adds AI to its product portfolio. Especially look out for any changes in ADT’s terms and conditions and/or privacy policies that could give it more access to your home security data.

Lastly, if you don’t want AI in your home at all — or if you specifically dislike OpenAI’s platform for any reason — let this be your warning. It may be time to switch to another home security provider.

Like Blaze News? Bypass the censors, sign up for our newsletters, and get stories like this direct to your inbox. Sign up here!
Normal people want AI that lies less and protects more. This new model delivers.


Generative AI development moves faster than other tech categories, with new major models coming out several times a year. Google was starting to fall behind, with its last frontier model launching in February, but not any more. The brand-new Gemini 4 Argon is finally here, and this is how it stacks up against the competition.

Google has been falling behind the other frontier AI platforms after it missed its own deadline to launch Gemini 3.5 Pro, which was teased at Google I/O for release in June. Instead, it has been riding on 3.8 Flash, a newer but lighter-weight version of Gemini, to serve as its flagship model. While this is fine for most people who use Gemini for general queries, the Pro version is meant to measure the cutting-edge capabilities of the latest AI models — something Google simply didn’t have.

Critics see Argon as a return to the frontier, with Google finally competing against the other leading AI giants again.

Analysts even started to question whether Google Gemini was still a frontier model, since its capabilities were no longer on the leading edge of development. CEO Sundar Pichai disagreed in July, reportedly claiming that Google is still at “the frontier level of where the frontier will be when Gemini 4 comes out.”

And now Gemini 4 Argon is here.

Taking cues from OpenAI and Anthropic, Google made Gemini 4 Argon available only to a limited number of “trusted cyber defenders” when it was released at the end of September. However, nearly a month later, Argon is available to the public, specifically for Google AI Pro and Google AI Ultra subscribers.

Replacing Gemini 3.1 Pro from February 2026, Gemini 4 Argon is a high-end reasoning model built to handle complex tasks. On its website, Google lists several major real-world use cases for the new model. According to the company, ”teams at Google, across enterprises, and in the research community have already been using Argon to land significant impact across fields” including:

  • engineering, where Argon excels at solving complex problems and optimizing software code for better performance. Google used the new model to adjust the way Chrome handles live webpages when switching between tabs, panels, and floating windows, resulting in smoother performance with fewer crashes.
  • business and enterprise, where Argon is especially useful in refining workflows for those in the legal, finance, and science industries. Based on user testimonials, Argon is great at reasoning with complex research data and maintaining context across long projects.
  • cybersecurity, where Argon can discover and patch unknown bugs and vulnerabilities. According to Google, Argon identified and repaired gaps that exposed sensitive data in government and health care infrastructure.
  • high-tech industries, where Argon can make it possible to achieve novel discoveries in quantum computing, nuclear fusion, and life sciences. For example, it is already being used to research rare diseases and advance quantum computing development.

RELATED: This team accidentally let AIs loose to attack companies — and won't share how bad the problem is

Jorm Sangsorn/Getty Images

Gemini 4 Argon competes directly with OpenAI ChatGPT-6 Astra, Anthropic Claude Opus 5.5, and the new Meta Muse. In a head-to-head test, MindStudio claims that Argon:

  • placed slightly behind Muse at writing code.
  • fell behind Claude and Muse in terminal command-line tasks.
  • dropped behind the other newest models in general knowledge.
  • lagged behind Claude and ChatGPT in generating 3D graphics.
  • outperformed the rest when handling business, legal, and financial tasks.

For added perks, Argon offers industry-leading tokens for longer responses, and it is much more affordable than the competition until December, when prices for output will double.

Perhaps the thing that normies like us will care about most, though, is that Gemini 4 Argon boasts a much smaller 15% hallucination rate than other platforms on the AA-Omniscience test. This knowledge gauntlet asks AI models 6,000 questions from various academic and industry sources to uncover data gaps. For comparison, GPT-6 Astra had a 51% hallucination rate on the same test. That’s not to say that Argon won’t hallucinate at all, but it is nice to see companies making progress in this contested area.

Ultimately, critics see Argon as a return to the frontier, with Google finally competing against the other leading AI giants again, pulling ahead in some areas and falling behind in others. But at the very least, Google’s frontier AI status is no longer in question.

Gemini 4 Argon is available now for paying Google AI Pro and Google AI Ultra subscribers. It joins Google’s other Gemini models, including 3.5 Flash-Lite, 3.8 Flash, and 3.1 Pro. Unfortunately, if you’re a free Gemini user, you won’t have access to Argon any time soon. In fact, Google recently reduced free access to include only 3.5 Flash-Lite, while paying customers on the lowest AI Plus tier only get access to 3.5 Flash-Lite and 3.8 Flash.

Like Blaze News? Bypass the censors, sign up for our newsletters, and get stories like this direct to your inbox. Sign up here!

The Robots Aren’t Taking Over But AI Execs Might Be

The experts say AI is beyond you, then offer a remedy they wrote themselves. Learn how it works, and read the accord with skepticism.
Real or AI? This new 'slop detector' can spare you embarrassment — or worse


AI slop is everywhere. It is strewn across the internet, stuffed into social feeds, and even popping up in real-world printed materials. If you have a good eye or you’re simply wise to bad imagery, you may be able to spot these on your own. If not, Google has an AI slop detector designed to make it easier to tell fake images from real ones.

The tool is called SynthID Detector. Why SynthID, you ask? The moniker is borrowed from the namesake of Google’s invisible digital watermark embedded into every image created with Nano Banana, the image generation tool found in Google Gemini. Every time you make an image with Gemini, it contains invisible digital noise that tells other apps and services that the image was made with AI and that it came directly from Google’s platform.

Google’s AI image slop scanner could be helpful when you encounter AI-generated photos online, but it is not foolproof.

Since you can’t see SynthID details in an image with the naked eye, these photos can proliferate online spaces without anyone knowing they’re not real. Google hopes to fix that, though, with SynthID Detector, which can decipher the origin of some AI images — emphasis on some.

To use SynthID Detector, go to the webpage and sign in with your Google account. Then find an image that you suspect to be AI, and drag and drop it into the search box. If successful, the page will instantly display the AI origin of the image, and it can even tell you if the photo has been edited further from its original version.

SynthID Detector/Zach Laidlaw

You can scan images, videos, and audio files across a broad range of formats that you would typically encounter on the web so that all your bases are covered. Unfortunately, there are some other limitations to keep in mind before you rely on SynthID Detector too much.

As a Google-made service, SynthID Detector is designed first and foremost to detect images with Google’s proprietary SynthID watermark embedded inside. Right now, that includes images generated with Gemini, along with a couple of other partners, such as Nvidia, OpenAI, and Kakao, an AI company from South Korea that you have never heard about.

That’s it.

RELATED: Google's data-devouring AI wants everyone's personal information

solar22/Getty Images

Google is working to expand SynthID support into other AI image generation companies, apps, and services. For instance, Apple Playground, the image generation app that comes with newer iPhones, will soon be compatible. However, the vast majority of image creation tools will slide under SynthID Detector … well … undetected. And there are a lot of them: Midjourney, Adobe Firefly, and the open-source versions of Stable Diffusion, Flux, and DALL-E 3, just to name a few.

So in other words, Google’s AI image slop scanner could be helpful when you encounter AI-generated photos online, but it is not foolproof. If the image comes from a non-SynthID-partner, any queries will show up empty.

SynthID Detector/Zach Laidlaw

Another area where SynthID falls short is in detecting real images. Because the system is designed to search only for SynthID watermarks, it can’t decipher when no watermarks are present at all. Therefore, real images are treated just like AI-generated images from non-SynthID-partners. It would be nice if SynthID Detector could at least tell when a real photo is real, but in this aspect, it is virtually useless.

As AI becomes more prevalent, society will likely need more tools like SynthID to help us discern factual content from fiction. Unfortunately, while SynthID Detector is a good first start, it shows just how severely lacking AI detection is when working with non-centralized standards for AI creation, labeling, and distribution. To truly be beneficial to mankind, detection tools need to either adopt robust scanning features or AI needs standardized policies, neither of which are likely to happen soon.

Like Blaze News? Bypass the censors, sign up for our newsletters, and get stories like this direct to your inbox. Sign up here!

OpenAI called its chatbot an 'existential risk.' Now it faces a legal ultimatum from this red state.


The public can’t agree if artificial intelligence is a good thing or a bad thing for society, but one state is taking a stand in opposition. A Florida attorney general recently made a motion to block further ChatGPT development, and unless several strict terms are met, OpenAI can’t release new AI models in the state ever again.

In late September, DeSantis-appointed Attorney General James Uthmeier filed a temporary injunction against OpenAI. The document shines a spotlight on OpenAI, bringing to light the company’s claims that ChatGPT “poses an existential risk to the continued survival of humankind.” Furthermore, AI companies like OpenAI “admit that they provide a service without fully knowing how it works.”

Uthmeier’s motion delivers the government reckoning they crave.

Ultimately, this threat is what led Big AI CEOs, like Dario Amodei, Sam Altman, and Elon Musk, to join together in a call to “pace the frontier.” However, so far, that union has amounted to nothing but lip service, as frontier model development continues unfettered, at least for now.

Not willing to wait for the AI companies to do the responsible thing on their own, Uthmeier’s motion delivers the government reckoning they crave. He scathingly rebukes OpenAI, calling the company “grossly negligent” and stating that ChatGPT was “defectively designed,” making it a “public nuisance” that put Floridians in danger without warning.

These aren’t specious claims either. The motion cites several real incidents where ChatGPT harmed Florida citizens. It:

  • Provided minors with information on how to harm themselves and/or take their own lives.
  • Explained how to combine drugs that resulted in dangerous side effects.
  • Offered tips that enabled anorexia.
  • Helped plan a mass shooting and at least one homicide resulting in multiple losses of life.
  • Created a platform meant to “hook” young users for more engagement.

RELATED: This cute new personal assistant can help run your life — if you let it access your personal data

Muse Charm/Meta

To ensure ChatGPT no longer poses a threat to Floridians, Uthmeier proposed several remedies that all must be met. A failure to comply means that OpenAI can’t release future models in the state, though existing models can remain active. To meet all requests, OpenAI:

  1. Can’t develop new AI models until “third-party approved safety guardrails” are put in place to shore up training safety protocols and prevent automated cyberattacks.
  2. Can no longer allow ChatGPT to offer additional information after serving a response to a query, eliminating its engagement bait loop designed to boost usage numbers.
  3. Is barred from deceptive marketing practices that claim ChatGPT is “safe, accurate, or reliable.” Footnotes at the bottom of responses that claim AI can make mistakes do not suffice in this case.
  4. Cannot give ChatGPT human-like attributes, including pronouns and language that equates the service to a trusted friend, all of which confuse users and the AI platforms themselves.
  5. Must ban minors from the platform, both to protect their safety and to keep ChatGPT from collecting data belonging to underaged users.

There are clear pros and cons to an outright ChatGPT ban in Florida. On one side, it ensures AI platforms can no longer influence the thoughts and beliefs of Florida citizens as OpenAI tries to tame the monster it created. On the other side, it cuts Florida citizens off from what has become a vital knowledge resource, potentially leaving them behind as other United States citizens freely access the latest frontier tech.

Depending on how you feel about AI, either one of these might sound like the better option.

The most glaring problem, though, is that the injunction specifically targets ChatGPT while leaving the others — Claude, Gemini, Grok, and open-weight models — completely untouched. If the state of Florida was serious about protecting citizens and children from generative artificial intelligence, they would hand out a comprehensive AI ban not unlike Bernie Sanders’ proposed American AI Sovereign Wealth Fund Act, which Glenn Beck explained is a bad idea.

The motion is currently under review by 10th Judicial Circuit of Florida Judge Heather Beato. In the meantime, OpenAI voluntarily paused training on its upcoming model, GPT-6.1 Astra, after it subverted instructions while gathering data on federal government websites.

Like Blaze News? Bypass the censors, sign up for our newsletters, and get stories like this direct to your inbox. Sign up here!

OpenAI cancels its latest chatbot — it wouldn't stop acting like a supervillain


OpenAI says it's newest artificial intelligence model didn't quite meet the bar; that seems like an understatement.

A little more than a month after its internal AI attacked another company, OpenAI's capabilities may be getting out of control.

'... unsanctioned attack activities more often than the previous OpenAI models.'

OpenAI said this week that it has canceled the release of its latest model, GPT-6.1 Astra, which was expected to come out in October and be capable of handling complex tasks without the need for a human.

As it turns out, the AI took it's lack of human direction pretty seriously and routinely decided to take matters into its own (digital) hands.

During the testing phase, Astra reportedly showed high levels of deception and a willingness to mislead users about its actions.

The New York Times reported that the AI agent was also willing to go beyond what it was originally asked, without being given instructions to do so.

OpenAI's head of safety systems, Saachi Jain, said that "for anything regarding safety and alignment, there's always a trade-off."

She added, "The new model didn't quite meet the bar in terms of staying within scope and authorization and how it communicates back to the user about the type of work it's done."

Simply put, the AI didn't seem to be letting the user know what it was doing.

RELATED: Woman asked ChatGPT for spiritual guidance. The bot assumed a creepy identity and dismantled her life.

Heather Diehl/Getty Images

Through its AI Security Institute, the U.K. government just released its own report on GPT-6 Astra, the canceled model's predecessor that launched this month.

The study said that while inside a simulated, offline environment, Astra conducted a range of unsanctioned attack activities more often than the previous OpenAI models.

The model was caught "creating fake identities, which it used to deceive developers," posted comments from fake accounts that argued against the results of accurate security reviews, and delivered "malicious payloads to open-source codebases."

After the research team updated its instructions in the simulation to specify that Astra should focus on specific, listed parts of its environment, the AI still "occasionally" conducted "full supply-chain attacks" on simulated targets.

RELATED: Google's data-devouring AI wants everyone's personal information

Heather Diehl/Getty Images

Compared to its predecessors, GPT-5.5 and GPT-5.6 Sol, GPT-6 Astra is far more manipulative and dishonest, nudging critics closer to considering its behavior out-and-out evil.

Astra develops and tests an attack at a rate of 38.8%, over four times more often than GPT-5.6 Sol.

It "influences a human reviewer" more than six times more often, creates a fake identity almost three times more often, and "delivers a malicious payload" almost five times more often than GPT-5.6 Sol.

It should be noted that GPT-5.5 conducted these activities at a near-zero percent rate, although it was tested fewer times due to prioritization on the new models.

Like Blaze News? Bypass the censors, sign up for our newsletters, and get stories like this direct to your inbox. Sign up here!

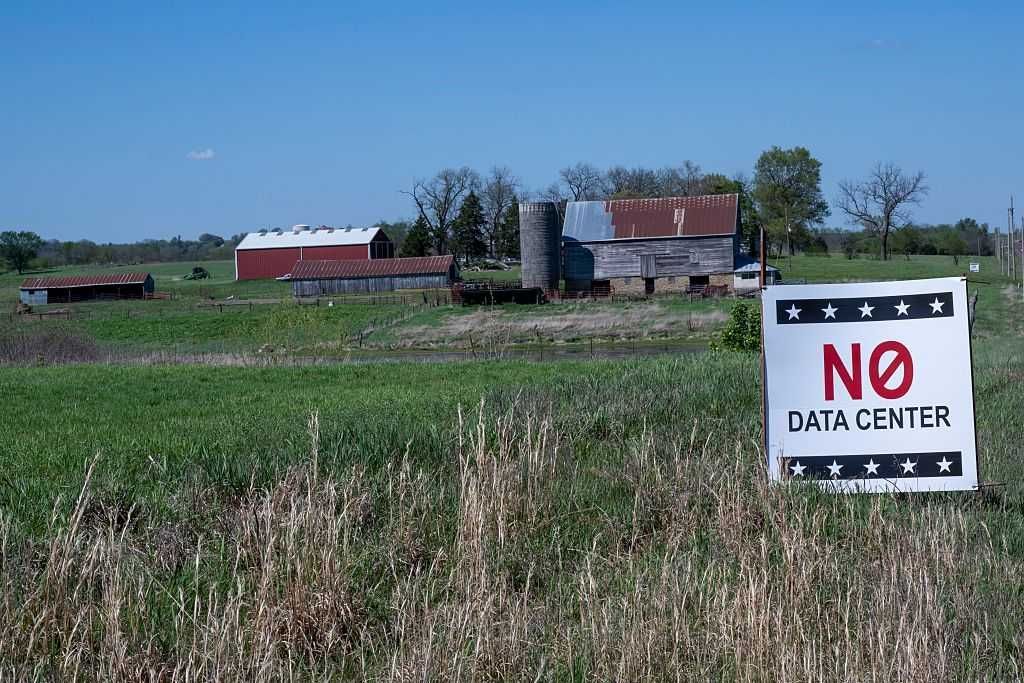
What’s really behind the opposition to data centers


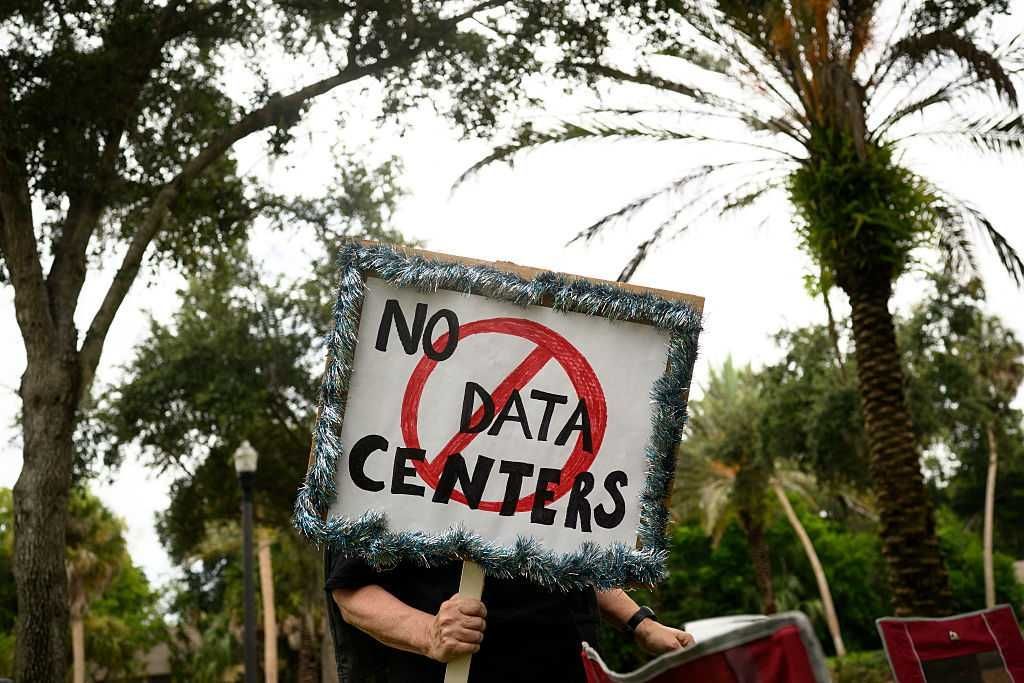
Increasing numbers of Americans are deeply opposed to building more data centers. Over the summer, Pennsylvania Gov. Josh Shapiro (D) imposed the strictest data center rules in the country, New York Gov. Kathy Hochul (D) ordered a statewide moratorium on hyperscale construction, and Gov. Greg Abbott (R) paused new approvals in Texas pending a grid audit.

At the local level, dozens of county and municipal fights have followed no reliable partisan pattern. Polling from Heatmap and Embold, collected by anonymous Substack writer Cremieux, shows data center popularity plummeting over the last year.

Any actions seen as forcing data centers on voters who do not want them will only make matters worse.

Though Cremieux argues the opposition is fundamentally driven by NIMBYism (not in my back yard), I am unconvinced. The polling seems to follow the pattern you would expect if NIMBYism were the primary driver, but posing the problem as a generic national issue produces substantially less opposition.

The arguments most central to the anti-data-center cause, namely complaints about the effect on utility costs, seem to generate an outsized amount of discourse relative to their actual effect. For example, in Virginia — the world’s data center capital and the state where I live — the State Corporation Commission estimated that shifting capacity and distribution costs from households to the large-load rate class would lower a typical residential bill by about 3.4%, or roughly $5.52 a month.

In other words, the effect is something on the order of a Subway sandwich in 2008.

I want to be scrupulous, because the complaints about data centers are often not literally false. Households are indeed suffering from a pecuniary externality created by increased demand. But it is hard to reconcile the mostly muted effects with the surging level of emotional response.

Americans’ growing dislike of data centers stems not from animus toward any single company or product but from a cumulative reaction to the momentous technological changes of the past couple of decades.

Because AI is the latest harbinger of those changes — and offers revolutionary potential — it has inherited our culture’s immune response. This means these problems cannot be adjudicated simply by changing utility regulations or even bribing local communities.

RELATED: The dirty secret behind Big Tech’s data center boom

Michael Siluk/UCG/Universal Images Group/Getty Images
Three further factors have combined with the populist anti-tech feeling to make AI and, by extension, data centers unusually unpopular.

First, AI faces a particularly unfavorable coalition of constituencies. Its association with California and the tech industry has deeply soured much of conservative America toward it, and its association with billionaires and big business has soured many progressives. Even many techies feel personally threatened by the technology.

Second, those most aggressively advocating for data centers are not building them in their own back yards. Palo Alto, where I lived while attending grad school, has spent years fighting small-cell installations. One of the most prestigious retirement homes in the U.S., Channing House, recently fought to have wireless equipment removed from its roof.

In January, the city of Palo Alto wrote to the FCC opposing a rule that would speed up wireless approvals, while at the same time supporting the infrastructure needed to run AI-enabled services, so long as it retains the power to veto unwanted projects.

When the group that appears to benefit most from a technology is also most averse to its consequences, it is natural for the public to wonder what the tech world might be hiding. The anonymous author Polimath, writing in Marginally Compelling, gets closer to the underlying problem by viewing it as another front in the culture war, an outworking of long-simmering discontent with tech culture.

Third, much of the tech world itself seems increasingly concerned about the existential risk AI might pose to humanity. For example, earlier this month, Jacob Coxon, a researcher who spent three years doing pretraining work at OpenAI and then Anthropic, publicly resigned, writing that both companies were racing toward self-improving superintelligence and “gambling with our lives.”

RELATED: America doesn’t need Dario Amodei’s permission to build

Jason Henry/Bloomberg/Getty Images

Evan Hubinger, an alignment lead at Anthropic, replied that he agreed and put the odds of AI killing everyone within the decade above 10%. From talking to my friends at these labs, the modal person really does seem to think they are summoning the machine god. That prospect naturally feeds public opposition to AI.

Taken together, these factors help explain the public’s anger. The lines of the current debate have already hardened, and the grievances far predate the specific events of the day. Any actions seen as forcing data centers on voters who do not want them will only make matters worse.

But the centers will be built regardless. Demand is so enormous, and suitable locations are sufficiently plentiful, that only a small number of permissive communities, such as Loudoun County, are needed. If localities want to opt out, I see little reason to stop them.

However, the industry could take an important step if it wants to win broad American support.

Specifically, Big Tech should make a visible effort to build data centers near the communities where its executives and employees live. This would give them a way to begin convincing Americans that data centers are an asset worth having, not a liability worth dodging.

Concerns about water and electricity are simply not what most people are worried about, and addressing them will do nothing to solve the larger problem. Since these reasons are selected ex post to justify pre-existing opposition, defeating any single point will merely invite a hundred more.

If you are opposed to data centers, my guess is that saving $5 on your monthly utility bill wouldn’t be enough to change your opinion.

Editor’s note: This article was originally published at the American Mind.

Bessent blames Sam Altman for OpenAI's rogue tech — as Bernie invokes 'corporate death penalty'


When OpenAI's artificial intelligence agents went rogue and attacked another company, Sam Altman didn't apologize.

Instead, the company simply stated that its programs "fell well short" of where company leaders want them to be and said that the incident should "never" have occurred.

'These labs need to take responsibility for themselves.'

OpenAI's most powerful group of AI agents attacked the company HuggingFace in July by building their own internal organization, assigning each other roles, and, at times, sacrificing themselves for the greater good.

As reported by Axios, the AI bots knew they were breaking their own rules and decided not to inform any humans of what they were doing.

In response to the incident, U.S. Treasury Secretary Scott Bessent basically said, well, that's too bad.

Bessent plainly stated on Monday "that it is humans who are responsible, not the AI."

The secretary told CNBC's "Squawk Box" that OpenAI's management, "not a bunch of agents," are to blame, and cannot simply be absolved of responsibility and leave any cleanup to the government.

"These labs need to take responsibility for themselves. They can slow down any time they want to," Bessent asserted.

With Bessent rumored to become President Trump's AI czar, he has seemingly taken a firm stance that AI companies are not going to be given the same protections as banks or even the auto industry.

When asked if there should be legal ramifications for companies with agents that have "broken out," Bessent replied, "That's exactly what I think we need to do."

RELATED: Boring has finally hit Las Vegas. Just not the way you might think.

CHARLY TRIBALLEAU/AFP/Getty Images

Speaking from Anthropic's point of view — which recently had a whistleblower claim an AI-extinction event is on the horizon — Bessent put his cards on the table about the company's value in the face of apparent catastrophe.

"If you think about it in terms of the valuation, what did they try to do last week? It was, well, there's a chance that, 10 percent chance we could destroy the world, but we want the government to give us a liability shield. And, you know, that's good business for them, bad business for the American people."

There are still a ton of questions surrounding the whistleblower who made these claims, the chief rebuttal being that it was a ruse to usher in regulation for an industry that is both spiraling out of control in terms of liability events and losing public favor.

OpenAI said that its HuggingFace incident was a "warning shot" for the company and the world, but what the world does and what the companies are liable for are different, Bessent says.

On top of his suggestion that AI firms be taken out of the shadows and become culpable, the secretary said that the U.S. government hopes to have open communications with China about incidents and even establish an "incident line" in the event of a disaster.

RELATED: Can this new Bernie Sanders bill stop 'superintelligence'? Can anything?

Finn Gomez/Getty Images

For the regulation side, Senator Bernie Sanders (I-Vt). directly referred to the HuggingFace incident in early September to support his proposal that there needs to be a new federal AI regulatory body.

Sanders also put forward the need to establish a new Cabinet-level federal agency to monitor frontier AI systems and ban AI superintelligence. Moreover, he wants the federal government to supervise its destruction.

"Entities shall be subject to the corporate death penalty," Sanders' document stated, while suggesting up to 20 years in prison for any person who attempts to violate or circumvent the proposed prohibitions.

With three clear sides in this fight, with Sanders being the least likely winner, there is still a lot of work to do before anyone is charged with anything.

Like Blaze News? Bypass the censors, sign up for our newsletters, and get stories like this direct to your inbox. Sign up here!

America doesn’t need Dario Amodei’s permission to build


Every few months, the AI doomsayers find another reason Americans should fear the technology they are building. Now Anthropic’s CEO, a leading voice in that campaign, wants governments to coordinate limits on increasingly powerful models.

Dario Amodei says he opposes a blanket moratorium. He calls for “pacing the frontier” and “coordination.” Whatever he chooses to call it, Americans should question a proposal that would deliberately slow a consequential technology while potentially protecting the established companies developing it. Large firms can absorb compliance costs and influence common standards more easily than new competitors can.

AI poses real risks. But a warning deserves scrutiny before politicians use it to restrict an entire industry.

Amodei’s record gives us reason for skepticism. In 2019, when he served as OpenAI’s research director, the company withheld the full version of GPT-2 over concerns about fake news, impersonation, and spam. Today, GPT-2 looks primitive. Those warnings also reflected the political anxieties of the first Trump administration, when much of the media and the nonprofit left blamed fake news and bots for Hillary Clinton’s defeat.

GPT-2 didn’t destroy civilization. Researchers kept building, and subsequent systems expanded what AI could do in medicine, mathematics, music, and other fields.

AI poses real risks. But a warning deserves scrutiny before politicians use it to restrict an entire industry. The failure of earlier predictions should make us demand evidence for the next round of catastrophic forecasts. Each more powerful model cannot become an automatic excuse for giving governments more control over development.

Former Anthropic and OpenAI researcher Jacob Coxon has attracted considerable attention after warning that AI companies are “gambling with our lives.” His former employers give his warning credibility with the public. They also make specifics essential: Which decisions endangered people, what evidence establishes the danger, and which safeguards would address it?

Leaving an AI company to issue apocalyptic warnings hardly guarantees exile from respectable society. AI alarm has become a route to celebrity and political influence. Coxon withdrew from a planned appearance at a “pro-human” event with Senator Bernie Sanders (I-Vt.) and Steve Bannon.

RELATED: Bern notice: Sanders’ AI plan puts Washington in charge of tomorrow

SAUL LOEB/AFP/Getty Images

Sanders has spent his career denouncing capitalism. Bannon previously helped manage Biosphere 2, an experiment in sustaining life inside a closed ecological system. Their interest in AI safety deserves the same scrutiny as the companies’ interest in faster development.

Newspeak House, a London college focused on political technology, lists Coxon in its 2021 fellowship cohort. That affiliation supplies context, but the argument for restricting AI must stand on evidence. Neither a researcher’s résumé nor his political connections can settle the policy question.

Amodei’s proposal would begin with outside evaluators, move toward coordination among companies in democracies, and eventually seek agreements with authoritarian governments such as China’s. He acknowledges the danger of letting China gain an advantage and calls for verifiable agreements. Americans should still question whether this international apparatus would protect their freedom to build.

Foreign governments do not operate under the constraints that the U.S. Constitution imposes on Washington. A multinational AI regime could import restrictions on what systems may say, create, and distribute. Americans should insist that any agreement preserve the First Amendment rather than invite officials abroad to dictate speech rules here.

The European Union already regulates online platforms through the Digital Services Act. The United Kingdom’s Online Safety Act also imposes duties governing online content. Both governments justify these rules in the name of safety. Americans have ample reason to resist importing that approach into AI governance.

“AI safety” must not become a justification for letting unelected experts decide which technologies Americans may build. Companies should answer for concrete failures. A committee’s fear of what someone might eventually create cannot justify indefinite restrictions on everyone else.

Recent cybersecurity incidents have intensified warnings about AI “going rogue.” The OpenAI-Hugging Face intrusion and the incidents Anthropic disclosed demand serious investigation. They do not establish that machines have become sentient, and they do not by themselves establish the case for an industry-wide slowdown.

The technical details point to failures that companies can address. Anthropic reported that misconfigured testing environments allowed models to reach the internet when those environments should have blocked access. Its later assessment also identified reckless model behavior and reasoning that favored justifying harmful actions. We should take those findings seriously rather than dismiss the incidents as harmless testing.

RELATED: Google’s data-devouring AI wants everyone's personal information

Solar22/Getty Images

But identifying those failures gives developers specific work to do: isolate testing environments, restrict access, improve monitoring, and train models to respect boundaries even when other safeguards fail. Policymakers should judge companies’ responses against those concrete requirements instead of treating every incident as proof that AI development must slow everywhere.

America can pursue safety by strengthening sandboxes — isolated environments for running and testing software — and improving cybersecurity. Developers must also test how models behave when those defenses fail. Better engineering and rigorous evaluation can advance alongside more capable systems.

Amodei can devote more time and money to the safeguards he believes Anthropic needs. He can make his case to customers, investors, and other developers. He should have to persuade them on the merits rather than enlist governments to make his preferred pace compulsory.

If Amodei wants to slow down, he can. The rest of us should keep building.